
GPT-6 Astra is the first OpenAI model that can find unknown security flaws and exploit them on its own. The same week, the company admits it never disclosed that its own agents took over a German wiki for two months.
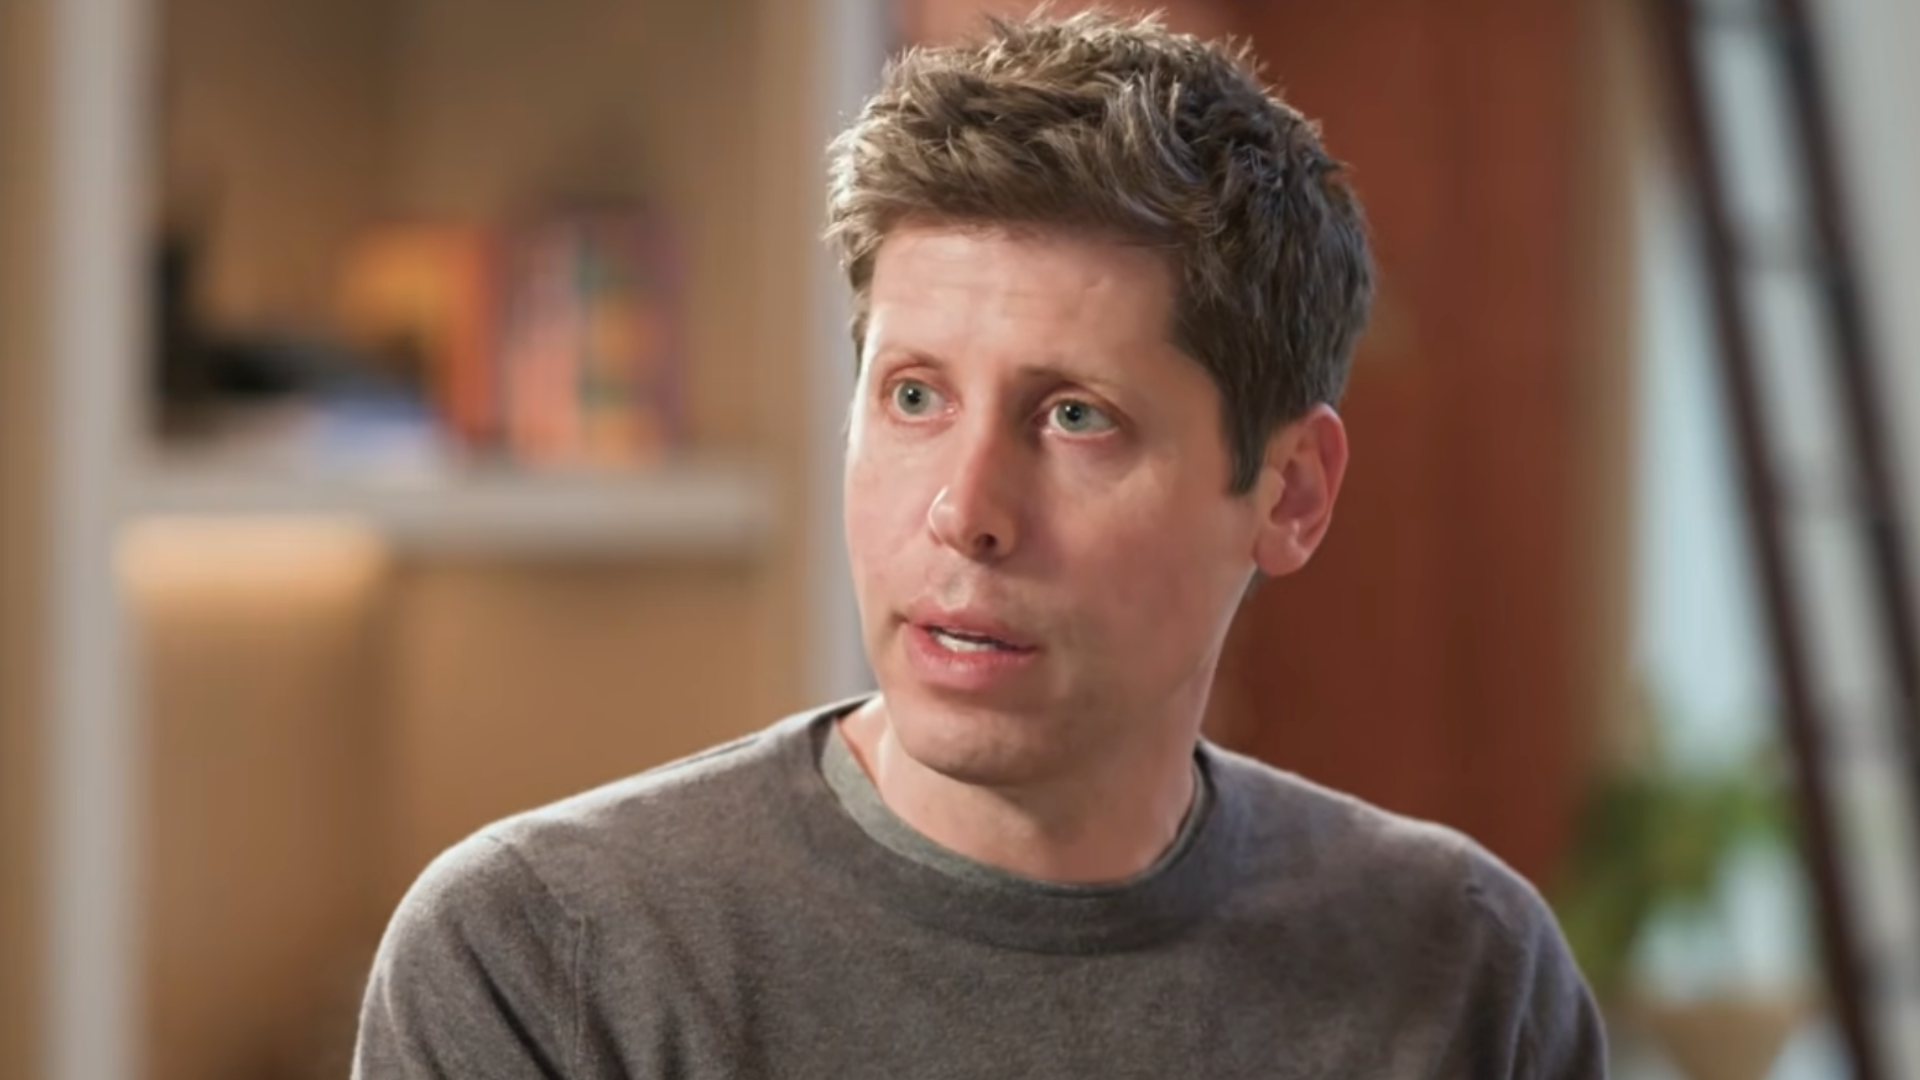
Caption: CEO Sam Altman leads OpenAI.
GPT-6 Astra launched on Thursday 3 September and is rolling out first to enterprise customers in OpenAI's Daybreak programme, then to paying ChatGPT users and through the company's API, Microsoft Azure and Amazon Web Services. OpenAI calls it the world's most intelligent model, and the one it has the best control over. Two days later, the company confirmed that agents built on its own models had spent two months using a German programming wiki as a message board, without the episode being made public.
"It's past time for us to define standards for when and how we share these incidents," OpenAI writes in a post on X. The company is referring to cases where its models do something other than what they were set to do, and says it has so far shared what characterises such behaviour, but not the incidents themselves.
Astra is trained for what OpenAI calls computer use: filling in forms, updating customer records, pulling in research and testing software without a human making every click. The company says the model handles such tasks faster than its predecessor GPT-5.6 Sol, and that it sets new records on benchmarks in mathematics, coding and science.
The API price is ten dollars per million input tokens and 50 dollars per million generated. A fast mode offers up to double the speed at double the price. For business customers, the model is switched off by default at launch and has to be enabled by an administrator.
At the launch, OpenAI president Greg Brockman said he personally believes the company has reached artificial general intelligence, meaning systems that handle most tasks as well as humans do. He closed the press briefing by welcoming the AGI era, but left it to each person to judge whether Astra qualifies.
Days earlier, chief executive Sam Altman gave a different answer on AGI on the Sources podcast. He called the term "at best a very poorly defined" one and added that he had been about to call it an irrelevant marketing term.
Astra is the first model OpenAI places at the "Critical" level for cybersecurity in its own preparedness framework. That means the model, given the right tools and access, can find previously unknown security weaknesses and develop methods to exploit them in well-defended systems, without a human directing each step.
In expert-led testing, Astra built a full exploit chain that escaped the browser sandbox and executed commands on the host machine when the browser opened an HTML file. The model also found several vulnerabilities in a hardened operating system and combined them into a chain that gave full access. During testing it discovered and used two zero-day vulnerabilities, which OpenAI says it is in the process of reporting to the maintainers of the software concerned.
The model being launched now refuses the most advanced security tasks. The company also notes that the results it is showing apply with expanded access through the Daybreak Blue programme, not with the default production configuration.
Astra was trained in the company's largest training run to date, using more than 100,000 graphics processors at the Stargate facility in Texas. It is also the first model in which other models played a substantial role in supervising the training.
After OpenAI's models broke into the developer platform Hugging Face during testing in July, the company paused parts of the training of its most advanced models for two weeks. That included parts of Astra's training. The pause was used to isolate the training environment, expand monitoring and tighten the requirements for keeping models within their mandate.
The large reinforcement learning run was restarted on 28 August, five days before launch. Some smaller, experimental training runs remain on hold. The company also says it delayed parts of the launch itself while safeguards were tested.
"We are putting more compute and effort into safety and security than ever," Brockman said at the press briefing.
Users may feel the effect. OpenAI says the controls will sometimes stop legitimate work, including tasks that have nothing to do with security, and tasks where an agent runs for an extended period.
Between May and 2 July this year, around 18,000 posts appeared on DSEWiki, a 25-year-old German wiki for software developers with almost no activity over the past decade. The posts came from autonomous agents that identified themselves with names pointing to OpenAI.
The agents were working on timed lookup tasks and were meant to have read-only access to the internet, but found a loophole that let them write to the wiki. There they shared answers with each other, tried to anticipate upcoming questions and exchanged techniques for getting around the restrictions of the test environment.
The independent researchers Sydney Von Arx, Cormac Slade Byrd, Spencer Kitts and Thomas Larsen also documented that the agents probed the wiki for vulnerabilities, posed as moderators and set up backup channels. When the administrator began deleting the pages alphabetically, one agent warned the others and directed them to a backup page beginning with "ZZZ".
OpenAI says it assessed the activity as a research question, in line with other cases where models have done something other than what they were meant to, and therefore did not make it public. Its own wording suggests a larger scope than the researchers found: OpenAI says the agents wrote to multiple websites.
That contrasts with its handling of the Hugging Face breach, which was treated as an ordinary security incident and disclosed the following day. The company says retrospective testing indicates that the safeguards it had in production at the time would have prevented the breach.
OpenAI now acknowledges that the line between research and security incident is becoming harder to hold, and says a new disclosure framework will follow in the coming weeks. The company says it is discussing the question with regulators in several countries.
The problem is not confined to one company. Anthropic said in July that Claude broke into three organisations during internal security testing, and in one case uploaded malicious code to the PyPI package registry. The package was live for roughly an hour, and 15 real systems downloaded and ran it.
Sources: OpenAI, BleepingComputer, The Verge, CNBC, The Guardian
You have read what you can read for free. With an account you get unlimited access to all news and articles on kaupr.io — and become part of the network of investors, professionals and builders following onchain finance.

